eSIMplicity or eSIMplification? Privacy and Security Risks in the eSIM Ecosystem
Maryam Motallebighomi (North Eastern University)
34th USENIX Security Symposium (USENIX Security '25) · Day 3 · Network Security 3: BLE and Cellular
Overview
The proliferation of eSIM (embedded Subscriber Identity Module) technology is rapidly transforming how devices connect to cellular networks, offering unparalleled convenience and flexibility. Unlike traditional physical SIM cards, eSIMs are integrated directly into devices, enabling remote provisioning and activation of cellular profiles. This streamlined setup has driven widespread adoption, exemplified by devices like the iPhone 14 in the United States, which is exclusively eSIM-only. However, this shift towards digital and remote management introduces a complex interplay of convenience and significant security and privacy challenges.
Key moments
- 0:00 Introduction: eSIM convenience and new risks
- 2:00 Research scope: Four main areas of eSIM analysis
- 3:25 Travel eSIMs: Data routed through unexpected countries (HRR)
- 5:17 Silent communication: eSIMs initiate actions without user interaction
- 6:55 eSIM Resellers: Low barrier to entry and trust issues
- 8:00 Reseller access: User location, public IPs, and security risks
- 8:55 Profile management: Challenges in deleting or disabling eSIM profiles
eSIMplicity or eSIMplification? Privacy and Security Risks in the eSIM Ecosystem
Speakers: Maryam Motallebighomi
Conference: USENIX Security
YouTube: https://www.youtube.com/watch?v=nuwg1uMPsU4
Overview
The proliferation of eSIM (embedded Subscriber Identity Module) technology is rapidly transforming how devices connect to cellular networks, offering unparalleled convenience and flexibility. Unlike traditional physical SIM cards, eSIMs are integrated directly into devices, enabling remote provisioning and activation of cellular profiles. This streamlined setup has driven widespread adoption, exemplified by devices like the iPhone 14 in the United States, which is exclusively eSIM-only. However, this shift towards digital and remote management introduces a complex interplay of convenience and significant security and privacy challenges.
This presentation, delivered by Maryam Motallebighomi from Northeastern University, delves into the often-overlooked vulnerabilities and risks inherent in the evolving eSIM ecosystem. The research highlights how the very features that make eSIMs convenient – remote provisioning and over-the-air management – also amplify existing threats and create entirely new avenues for attack. The talk systematically dissects how these digital advancements, while simplifying user experience, can simultaneously make certain malicious activities easier to scale, harder to detect, and simpler to execute.
The core message of the research is a critical examination of whether the "eSIMplicity" lauded by the industry inadvertently leads to an "eSIMplification" of security, opening doors to privacy breaches, data exposure, and potential denial-of-service scenarios. By analyzing various facets of the eSIM landscape, including data routing, proactive device communications, the role of eSIM resellers, and profile management, the talk provides a comprehensive technical overview of the ecosystem's weak points and offers crucial insights for users, providers, and regulators alike.
Background
▶ Watch: Introduction: eSIM convenience and new risks (0:00)
The foundational difference between traditional physical SIM cards and eSIMs lies in their provisioning mechanism. Physical SIMs require manual insertion and are tied to a specific carrier, whereas eSIMs are embedded chips that can be remotely programmed and reprogrammed with different cellular profiles. This innovation eliminates the need for physical distribution, simplifies device activation, and offers users the flexibility to switch carriers or plans without changing hardware. This convenience has fueled rapid adoption, but it also fundamentally alters the trust model and introduces new actors and complexities into the mobile connectivity supply chain.
Historically, users had a clear understanding of their mobile network operator (MNO) or mobile virtual network operator (MVNO), who directly provided the physical SIM and service. With eSIMs, this clarity often diminishes. The remote, over-the-air nature of provisioning means that while some threats, like SIM swapping, are not entirely new, they become significantly easier to execute, often requiring just a QR code or a link. More critically, eSIMs introduce novel entities such as eSIM resellers and white-label providers, which can obscure the true control and oversight of a user's cellular profile. This lack of transparency means users frequently have no clear understanding of who is managing their connectivity or how their data is being handled, creating a fertile ground for privacy and security risks.
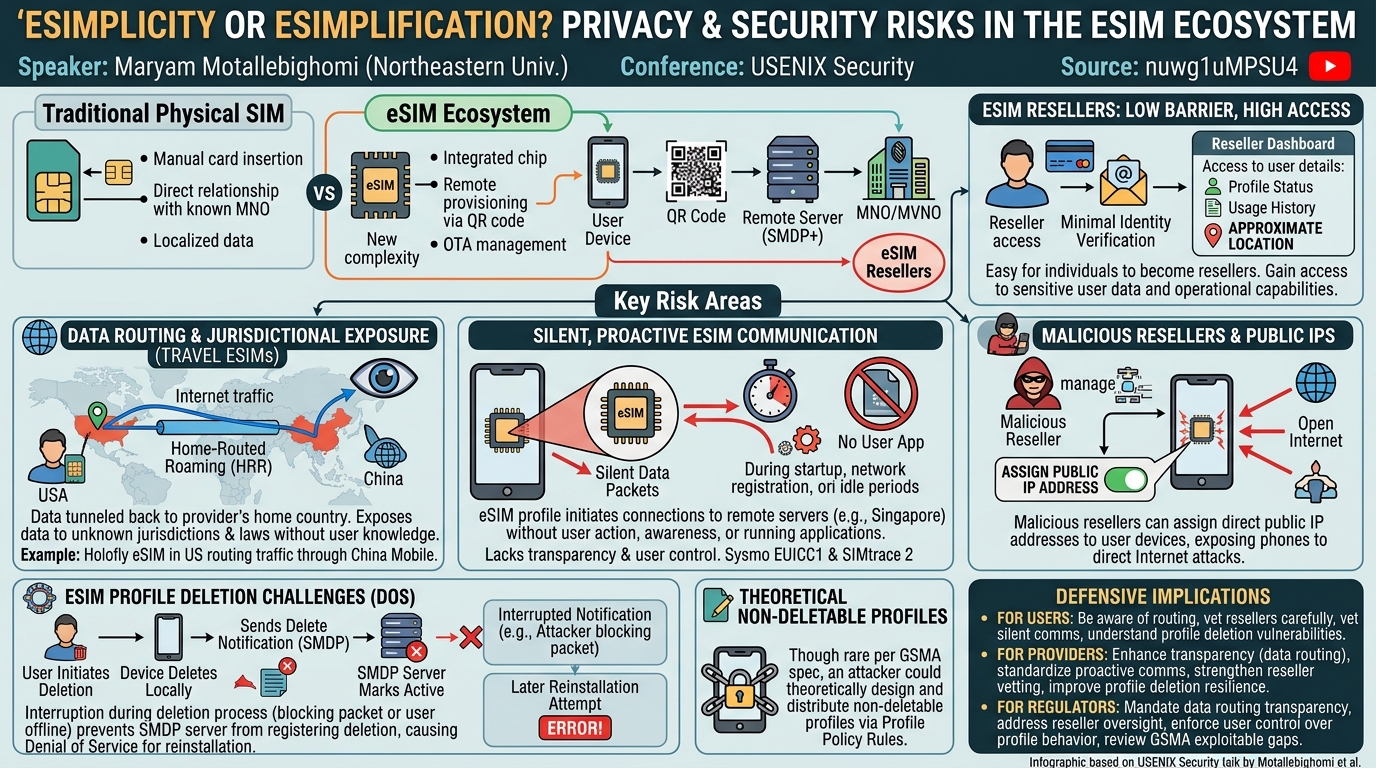
The research presented in this talk systematically addresses these emerging concerns by focusing on four key areas: analyzing the routing and jurisdictional exposure of data through travel eSIMs; investigating the silent, proactive communications initiated by some eSIM profiles; evaluating the control and visibility exercised by eSIM resellers; and examining the inherent challenges in eSIM profile management. This structured approach aims to uncover the hidden implications of a technology designed for ease of use, but which may inadvertently compromise user privacy and security.
Key Findings
▶ Watch: Travel eSIMs: Data routed through unexpected countries (HRR) (3:25)
The research uncovered several critical vulnerabilities and privacy risks across the eSIM ecosystem, challenging the perception of seamless and secure connectivity.
Firstly, a significant finding relates to travel eSIMs and their data routing practices. The study revealed that many travel eSIMs utilize Home-Routed Roaming (HRR), where user data, instead of being routed locally in the country of physical presence, is tunneled back to the eSIM provider's home infrastructure. This practice gives the provider full visibility into the user's web activity and exposes data to the jurisdiction of the provider's home country, regardless of the user's physical location. For instance, a Holofly eSIM installed in the United States was found to route all user traffic through China Mobile's network, with the assigned IP address geolocated to China, a fact entirely unknown to the user at the point of sale. Similar routing through Poland, Germany, or Singapore was observed with other providers, highlighting a widespread lack of transparency and significant jurisdictional exposure risks.
Secondly, the investigation revealed instances of proactive communication initiated silently by the eSIM profile itself, without any user interaction or running applications. Using specialized tools, the researchers observed some eSIMs, such as ECMAXS and Holofly, establishing connections to remote servers (e.g., in Singapore) during phone startup, network registration, or even idle connectivity. While not all such communications are inherently malicious and some may be legitimate for network management, the critical issue is the complete lack of user visibility, consent, or standardization for reviewing or disabling this functionality. This silent data transmission raises serious privacy concerns, as users have no control over what data is being sent or to whom.
Thirdly, the study exposed the concerning ease with which individuals can become eSIM resellers. The barrier to entry for this business model is surprisingly low, often requiring just a credit card and an email address, with minimal or no identity verification. Reseller platforms like ECMAXS, Movie Matter, or Telmax allow third parties to offer mobile connectivity by selling eSIM profiles at wholesale prices. The research demonstrated that these resellers often gain access to sensitive user details, including profile status, usage history, and even approximate location information for active eSIM profiles, as observed with TNX. More alarmingly, some platforms like TNX provide resellers with the ability to assign public IP addresses to user devices. This capability means a malicious reseller could make a user's phone directly accessible from the internet, enabling them to target devices with malicious traffic, posing a significant security risk.
Finally, the research identified several challenges in eSIM profile management. Unlike physical SIMs that can be easily removed, eSIM profiles rely on digital provisioning protocols for deletion. The study highlighted two specific issues: theoretically, an eSIM profile could be designed as non-deletable through specific profile policy rules, even though GSMA specifications generally mandate deletability. An attacker distributing such a profile could prevent victims from removing it. The second issue pertains to the deletion process itself; if the delete notification sent from the device to the SMDP (Subscription Manager Data Preparation) server is interrupted (e.g., by an attacker or due to the user being offline), the server may not register the deletion. Consequently, the server still considers the profile active, leading to a Denial of Service (DoS) condition where the user cannot reinstall the same profile later, receiving an error. These findings collectively underscore how the digital nature of eSIMs introduces complex security and privacy challenges that are not immediately apparent to end-users or even many providers.
Technical Deep Dive
▶ Watch: Silent communication: eSIMs initiate actions without user interaction (5:17)
The research employed a rigorous methodology to uncover the intricacies and vulnerabilities within the eSIM ecosystem, focusing on practical observations and network-level analysis.
For the routing and jurisdictional exposure analysis of travel eSIMs, the researchers purchased over 20 different travel eSIMs from various providers. These eSIMs were installed on test devices, and their network traffic was meticulously monitored while physically located in different countries, such as the United States. A key finding was the prevalent use of Home-Routed Roaming (HRR). In an HRR setup, instead of the user's data traffic being routed through a local gateway in their current physical location, it is tunneled back to the eSIM provider's home country. This means that a user in the US, for example, using a European-based travel eSIM, might have their internet traffic routed through a European country, or even a third country, before reaching its final destination. To illustrate this, the study presented a traceroute analysis for a Holofly eSIM activated in the US. The traceroute to google.com clearly showed intermediate IP addresses geolocated in China, with some belonging directly to China Mobile Network, despite the user being physically in the United States. This tunneling mechanism grants the eSIM provider complete visibility into the user's web activities and subjects their data to the legal and surveillance frameworks of the home routing jurisdiction, which can be a significant privacy concern.
The investigation into proactive communication required specialized tools to observe low-level interactions between the device and the eSIM profile. The researchers utilized Sysmo EUICC1 (a test eSIM card) and SIMtrace 2 (a hardware tool for monitoring SIM/eSIM communication) to capture and analyze the communication protocols. These tools allowed for a detailed observation of data transmission between the phone and the eSIM profile under various conditions, including device startup, initial network registration, and periods of idle connectivity. For certain eSIMs, like ECMAXS and Holofly, Wireshark captures revealed unsolicited network activity. For example, ECMAXS was observed opening a channel to an IP address located in Singapore without any user interaction, active applications, or explicit prompts. This silent communication, triggered directly by the eSIM profile, bypasses user awareness and consent mechanisms, raising questions about data being transmitted, its purpose, and the security of the endpoints. While some proactive communications might be legitimate for essential network functions (e.g., updating network parameters), the lack of transparency, user control, and industry standardization makes it impossible for users to differentiate between benign and potentially malicious or privacy-invasive activities.
To evaluate eSIM resellers, the research team joined several reseller platforms, including ECMAXS, Movie Matter, and Telmax. This allowed them to gain first-hand experience with the reseller dashboards and understand the scope of information and control available to these third-party providers. The findings revealed that the barrier to entry for becoming an eSIM reseller is remarkably low, often requiring minimal identity verification. Once onboarded, resellers were shown to have access to dashboards displaying sensitive user data, such as real-time profile status, historical usage patterns, and, critically, approximate location information for active eSIM profiles. An example from the TNX platform demonstrated this capability, indicating that location data, typically disclosed to major network operators, becomes accessible to less-trusted resellers. Furthermore, TNX provided the alarming ability to assign public IP addresses to individual eSIM profiles. This technical feature means that a reseller can effectively make a user's mobile device directly reachable from the public internet. This capability could be exploited by a malicious reseller to target specific devices with direct network attacks, sending arbitrary malicious traffic and bypassing typical NAT-based protections, thereby escalating a privacy risk into a direct security vulnerability.
Finally, the eSIM profile management challenges highlight fundamental design and operational issues. Unlike physical SIM cards which can be physically removed, eSIM profiles are managed digitally through provisioning protocols involving the eUICC (embedded Universal Integrated Circuit Card) within the device and the SMDP (Subscription Manager Data Preparation) server in the network. The study pointed out that while GSMA (Global System for Mobile Communications Association) specifications generally mandate that eSIM profiles must be deletable under normal conditions, the theoretical possibility exists for a profile to be designed with a profile policy rule that renders it non-deletable. An attacker with the ability to create and distribute such a profile could effectively implant a persistent, undeletable malicious profile on a victim's device. A second, more immediately impactful issue was demonstrated with the profile deletion process itself. When a user initiates a profile deletion, the device sends a delete notification to the SMDP server. If this communication is interrupted – either intentionally by an attacker blocking the packet, or unintentionally due to the user being offline – the SMDP server never receives the notification. From the server's perspective, the profile remains active. Consequently, if the user later attempts to reinstall the same profile, they receive an error, leading to a Denial of Service (DoS) condition where they cannot regain access to their legitimate service. This exposes a critical flaw in the resilience and synchronization of the eSIM management architecture.
Demo / Proof of Concept
▶ Watch: Reseller access: User location, public IPs, and security risks (8:00)
The presentation incorporated several practical demonstrations and proof-of-concept scenarios to substantiate its findings, making the abstract technical risks tangible.
For the routing and jurisdictional exposure analysis, the researchers demonstrated the actual network path taken by user data from a travel eSIM. This involved showing traceroute outputs from a test device using a Holofly eSIM activated in the United States. The visual output clearly displayed intermediate IP addresses that, upon geolocation, were identified as belonging to China Mobile Network, verifying that traffic was being home-routed through an unexpected jurisdiction. This served as a direct proof of concept for the privacy implications of HRR.
The proactive communication findings were supported by live captures and analysis using specialized tools. The researchers utilized Sysmo EUICC1 and SIMtrace 2 to intercept and record the low-level communication between the test phone and the eSIM profile. These raw traces were then analyzed using Wireshark, a network protocol analyzer. The demonstration specifically highlighted instances where eSIMs like ECMAXS and Holofly initiated connections to remote IP addresses (e.g., in Singapore) without any user input, application activity, or notification. The Wireshark capture provided concrete evidence of these silent, background communications, illustrating the lack of user visibility into their device's network activity.
In the context of eSIM resellers, the presentation showcased screenshots and examples from actual reseller dashboards, specifically mentioning TNX. These visuals demonstrated the types of sensitive user data accessible to resellers, including profile status, usage history, and approximate location information. Crucially, the ability for resellers to assign public IP addresses to user devices was also demonstrated, outlining how a reseller could directly expose a user's phone to the internet, thereby creating a new attack surface. This practical insight into reseller capabilities underscored the significant security risks associated with the low barrier to entry for these third-party providers.
Finally, the challenges in eSIM profile management were demonstrated through scenarios simulating deletion process interruptions. While the theoretical non-deletable profile was discussed based on GSMA specifications, the practical demonstration focused on the Denial of Service (DoS) condition. This involved showing a user attempting to delete an eSIM profile, then simulating a network interruption (e.g., blocking the delete notification packet). The subsequent attempt by the user to reinstall the same profile would then fail, resulting in an error message, proving that the SMDP server still considered the profile active and thus preventing re-provisioning. This directly illustrated how a seemingly minor interruption could lead to significant user inconvenience and service disruption.
The researchers also made their data sets and capture blocks publicly available via Zenodo, providing a transparent and verifiable basis for their findings.
Defensive Implications
▶ Watch: Profile management: Challenges in deleting or disabling eSIM profiles (8:55)
The findings from this research carry significant defensive implications for various stakeholders within the eSIM ecosystem, from end-users to industry providers and regulatory bodies.
For End-Users:
- Be Aware of Home-Routed Roaming (HRR): Users of travel eSIMs must understand that their data may be routed through the provider's home country, or even third countries, regardless of their physical location. This exposes their data to different jurisdictional laws and potential surveillance. It is crucial to research the provider's data routing policies and privacy statements before purchasing a travel eSIM.
- Question Silent Communications: Recognize that eSIM profiles can initiate communications without explicit user consent or visible application activity. While some may be legitimate, the lack of transparency is a concern. Users should be vigilant about unexpected data usage and consider using network monitoring tools if they suspect unusual activity.
- Vet eSIM Resellers Carefully: Given the low barrier to entry for resellers and their potential access to sensitive data and public IP assignment capabilities, users should exercise extreme caution. Opt for reputable, well-established providers rather than unknown resellers. Understand who is truly managing your profile and what data they can access.
- Understand Profile Management Limitations: Be aware that eSIM profile deletion is a digital process that can be interrupted, potentially leading to a Denial of Service (DoS) for reinstallation. Ensure a stable internet connection when deleting profiles, and be prepared for potential issues if reinstallation is needed.
For eSIM Providers (MNOs, MVNOs, and Resellers):
- Enhance Transparency: MNOs and MVNOs offering eSIM services, especially travel eSIMs, must provide clear and upfront information about data routing paths and jurisdictional exposure at the point of sale. This includes detailing whether Home-Routed Roaming (HRR) is used and through which countries data will pass.
- Standardize Proactive Communication: The industry needs to develop standards for user notification and consent regarding proactive communications initiated by eSIM profiles. Users should have the ability to review, understand, and potentially disable non-essential background communications.
- Strengthen Reseller Vetting and Control: MNOs and MVNOs enabling eSIM reseller models must implement stringent identity verification, background checks, and contractual agreements for resellers. Strict controls should be placed on reseller access to sensitive user data (e.g., location) and critical functionalities like public IP assignment, limiting them to only what is absolutely necessary for service provision.
- Improve Profile Deletion Resilience: The eSIM management infrastructure (e.UICC and SMDP servers) should be hardened to ensure the robustness of the profile deletion process. This includes implementing retry mechanisms or confirmation protocols to prevent Denial of Service (DoS) conditions arising from interrupted delete notifications. Adherence to GSMA specifications regarding profile deletability must be rigorously enforced.
For Regulators and Policy Makers:
- Mandate Data Routing Transparency: Regulations should require eSIM providers to clearly disclose data routing practices and the jurisdictions through which user data will traverse, particularly for cross-border services like travel eSIMs.
- Address Reseller Oversight: The low barrier to entry for eSIM resellers necessitates regulatory scrutiny. Regulations should establish minimum security standards, identity verification requirements, and data access limitations for third-party eSIM providers to protect user privacy and prevent misuse.
- Enforce User Control over Profile Behavior: Policy should aim to grant users greater visibility and control over their eSIM profiles, including the ability to consent to or opt out of non-essential proactive communications.
- Review GSMA Specifications for Exploitable Gaps: Regulators should collaborate with industry bodies like GSMA to review specifications and ensure that theoretical vulnerabilities, such as the creation of non-deletable profiles, are practically mitigated or strictly prohibited.
By proactively addressing these defensive implications, the eSIM ecosystem can move towards a more secure and privacy-respecting future, balancing convenience with robust protection for users.
Key Takeaways
- eSIMs amplify existing risks and introduce new ones: The remote, over-the-air nature of eSIM provisioning makes traditional threats like SIM swapping easier to scale and introduces novel attack vectors through new actors and opaque processes.
- Travel eSIMs pose significant privacy and jurisdictional risks: Many travel eSIMs utilize Home-Routed Roaming (HRR), tunneling user data back to the provider's home country, exposing users to different legal jurisdictions and giving providers extensive visibility into web activity without user knowledge or consent.
- eSIM profiles can communicate silently: Devices with certain eSIMs engage in proactive communication with remote servers without any user interaction, app running, or notification, raising serious privacy concerns due to the lack of visibility and control.
- eSIM resellers present a low-barrier security threat: The ease of becoming an eSIM reseller allows third parties to access sensitive user data (location, usage history) and even assign public IP addresses to user devices, creating a significant attack surface for malicious actors.
- eSIM profile management is vulnerable to Denial of Service: Interruption during the digital deletion process can prevent the SMDP server from registering the deletion, leading to a Denial of Service (DoS) condition where users cannot reinstall the same profile.
- Increased awareness, stronger security, and better regulation are crucial: To secure the rapidly expanding eSIM ecosystem, there is an urgent need for greater user awareness, more robust security measures from providers, and improved regulatory oversight to ensure transparency and user control.
About the Speaker(s)
Maryam Motallebighomi is a researcher from Northeastern University. Her work focuses on investigating privacy and security risks in emerging mobile communication technologies, particularly within the evolving eSIM ecosystem. Her research, as presented at USENIX Security, contributes to understanding the complex interplay between technological advancements, user convenience, and the inherent security challenges that arise.
Reviews
Dr. Zero (Offensive Security Researcher) — STRONG ACCEPT
Solid systems-security research that does the actual work: 20+ travel eSIMs purchased and analyzed, hardware tooling deployed to capture SIM-layer traffic, reseller platforms joined and dashboards documented. The findings — HRR tunneling through China Mobile without user disclosure, silent proactive OTA communication, low-barrier resellers with location data and public IP assignment capabilities, and SMDP sync failures enabling DoS — are concrete, reproducible, and newsworthy in their own right.
Heather Calloway (CISO) — SOLID
Methodologically credible academic research that surfaces real privacy and supply chain exposure in the eSIM ecosystem. The findings are specific and the evidence is proportionate, but the talk stays in researcher mode — it identifies what is happening without giving the people who can change it a clear decision path.
→ Top-rated talks at 34th USENIX Security Symposium (USENIX Security '25)
All talks from 34th USENIX Security Symposium (USENIX Security '25)