DMAAUTH: A Lightweight Pointer Integrity-based Secure Architecture to Defeat DMA Attacks
Xingkai Wang
33rd USENIX Security Symposium · Day 1 · USENIX Security '24 · USENIX Security '24
Overview
This talk introduces DMAUTH, a novel hardware-software co-design architecture aimed at effectively defeating Direct Memory Access (DMA) attacks. Presented by Xingkai Wang at USENIX Security '24, the research addresses critical limitations in existing DMA protection mechanisms, particularly the Input/Output Memory Management Unit (IOMMU). DMA attacks represent a long-standing and potent threat, allowing malicious peripherals to bypass CPU oversight and directly manipulate system memory, potentially leading to privilege escalation, data exfiltration, or complete system compromise. While IOMMUs provide a foundational layer of defense, they are susceptible to sophisticated attacks that exploit inherent spatial and temporal vulnerabilities arising from their page-granularity memory management.
Key moments
- 1:30 IOMMU limitations and vulnerabilities to DMA attacks
- 2:50 Characterizing DMA behavior for effective design
- 4:00 DMATH's hardware-software co-design workflow
- 6:00 Arithmetic capable pointer authentication innovation
- 7:00 Resolving spatial and temporal DMA vulnerabilities
- 8:00 FPGA implementation and research framework
- 9:00 DMATH's low overhead evaluation results
DMAUTH: A Lightweight Pointer Integrity-based Secure Architecture to Defeat DMA Attacks
Speakers: Xingkai Wang
Conference: USENIX Security '24
YouTube: https://www.youtube.com/watch?v=kc3qtpWkrkQ
Overview
This talk introduces DMAUTH, a novel hardware-software co-design architecture aimed at effectively defeating Direct Memory Access (DMA) attacks. Presented by Xingkai Wang at USENIX Security '24, the research addresses critical limitations in existing DMA protection mechanisms, particularly the Input/Output Memory Management Unit (IOMMU). DMA attacks represent a long-standing and potent threat, allowing malicious peripherals to bypass CPU oversight and directly manipulate system memory, potentially leading to privilege escalation, data exfiltration, or complete system compromise. While IOMMUs provide a foundational layer of defense, they are susceptible to sophisticated attacks that exploit inherent spatial and temporal vulnerabilities arising from their page-granularity memory management.
DMAUTH proposes a robust solution built upon pointer authentication and fine-grained bounds checking, delivered through a transparent hardware authenticator placed directly on the system bus. The core innovation lies in its ability to enforce byte-grain memory access control and immediately invalidate outdated DMA pointers, thereby mitigating the spatial and temporal vulnerabilities that plague IOMMUs. By integrating these security features into a co-design that requires zero driver modifications and demonstrates remarkably low performance overhead, DMAUTH presents a practical and highly effective path forward for securing modern computing systems against a persistent class of hardware-level threats.
The significance of this work cannot be overstated. As systems become more complex and rely heavily on high-speed peripherals, the attack surface for DMA-based exploits continues to grow. DMAUTH offers a fundamental shift in how DMA security is approached, moving beyond coarse-grained page protections to a more granular and dynamic enforcement model. Its demonstrated efficiency and transparency make it a compelling candidate for integration into future System-on-Chip (SoC) designs, promising a significantly enhanced security posture without compromising system performance or requiring extensive re-engineering of existing software stacks.
Background
▶ Watch: IOMMU limitations and vulnerabilities to DMA attacks (1:30)
Direct Memory Access (DMA) is a fundamental technology in modern computing, enabling peripheral hardware components to directly access main memory without requiring CPU intervention. This capability is crucial for high-performance I/O operations, allowing devices like network cards, storage controllers, and graphics processors to efficiently transfer large volumes of data. Common interfaces supporting DMA include FireWire, Thunderbolt, and the ubiquitous PCI Express (PCIe) bus. While essential for system performance, DMA presents a significant security challenge: if a peripheral is compromised or malicious, its ability to directly read from or write to arbitrary memory locations can be exploited to corrupt data, inject malicious code, or gain full control over the system. Real-world DMA vulnerabilities have been exploited over decades, demonstrating the persistent nature of this threat.
Traditional memory protection mechanisms, such as the Memory Management Unit (MMU), virtualize physical addresses for user programs, restricting them to their mapped memory regions. However, the MMU does not restrict DMA access, leaving the door open for peripheral-initiated attacks. The de facto defense against DMA attacks is the Input/Output Memory Management Unit (IOMMU). An IOMMU maps physical memory to an I/O virtual address space, allowing peripherals to perform DMA operations only within these virtualized and permission-controlled regions. This significantly enhances memory security by providing a layer of isolation between peripherals and the main memory.
Despite its benefits, the IOMMU suffers from two critical limitations that sophisticated DMA attacks can exploit:
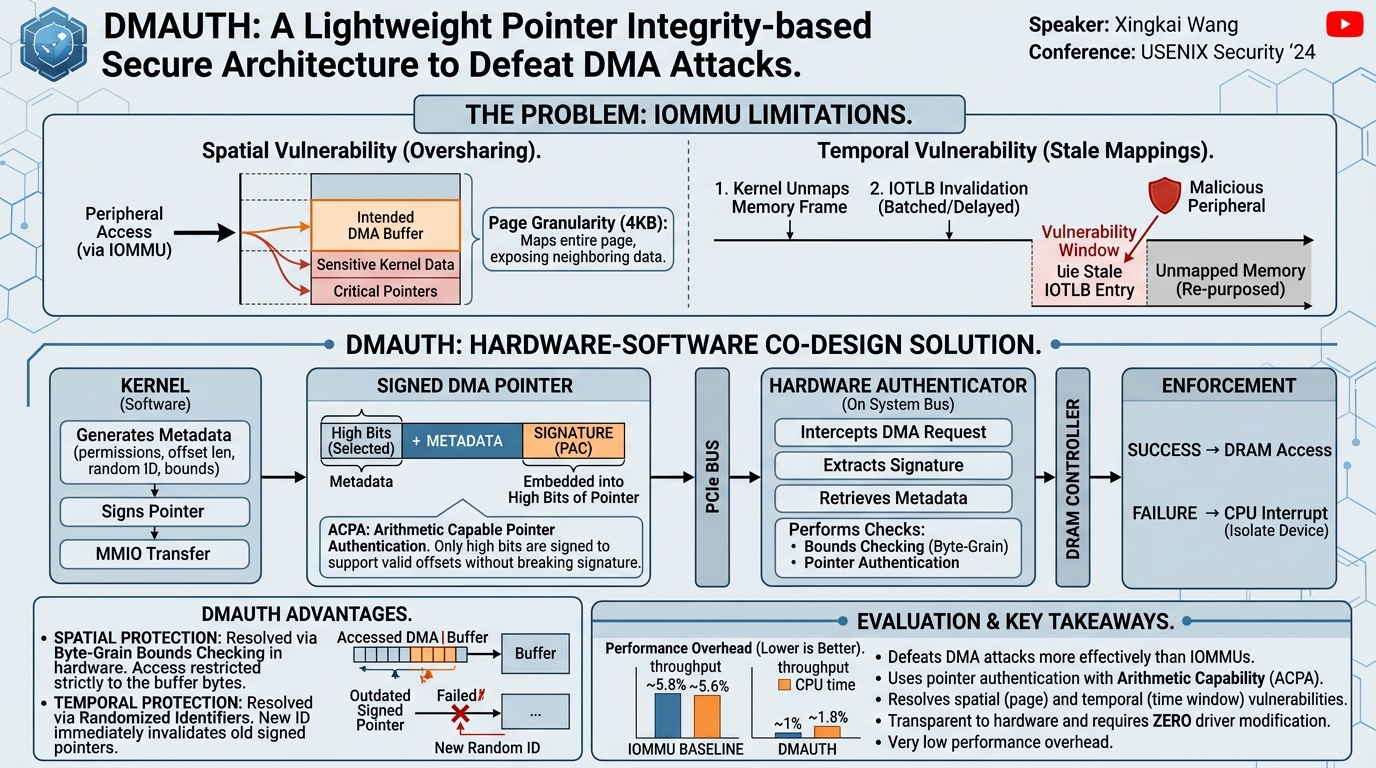
- Spatial Vulnerability: Like the MMU, the IOMMU manages memory at page granularity. When a buffer is mapped for a peripheral, the entire physical memory page containing that buffer is exposed. This means that if sensitive kernel data, other pointers, or critical control structures reside within the same page but outside the intended DMA buffer, they become directly accessible to the peripheral. This "oversharing" of memory within a page constitutes a spatial vulnerability, allowing an attacker to read or modify unintended data.
- Temporal Vulnerability: IOMMUs use an I/O Translation Lookaside Buffer (IOTLB) to cache address translations and accelerate performance. However, invalidation of IOTLB entries is often batched for efficiency, rather than immediate. This creates a time window where, even after a memory frame has been unmapped by the kernel, its mapping might still persist in the IOTLB. During this window, a malicious peripheral can continue to access the "unmapped" memory region, leading to a temporal vulnerability where stale mappings can be exploited.
These limitations mean that while IOMMUs provide a necessary layer of defense, they cannot effectively defeat elaborate DMA attacks that specifically target these spatial and temporal weaknesses. A truly effective solution requires stronger spatial and temporal guarantees, while also being transparent to existing hardware and drivers, and introducing minimal overhead in both throughput and CPU time.
To address these challenges, the researchers first characterized the DMA behavior of various devices. Their findings revealed several key insights that informed the design of DMAUTH:
- Most DMA operations do not solely use the start address of a buffer but rather involve an offset, indicating the need to support pointer arithmetic.
- The number of coexisting DMA buffers is typically limited, often just a few hundred, suggesting that managing metadata for these buffers is feasible.
- A significant majority of DMA buffers are not page-sized, directly contributing to the spatial vulnerability when IOMMUs map entire pages. These empirical observations highlighted the specific architectural requirements for a new, more robust DMA protection mechanism.
Key Findings
▶ Watch: DMATH's hardware-software co-design workflow (4:00)
The central contribution of this work is DMAUTH, a novel hardware-software co-design mechanism engineered to overcome the inherent limitations of IOMMUs and provide robust protection against DMA attacks. DMAUTH's core innovation lies in its application of pointer authentication to DMA pointers, managed by the kernel, and enforced by a dedicated hardware authenticator on the system bus.
The main discoveries and results can be summarized as follows:
- Pointer Authentication for DMA: DMAUTH leverages the concept of pointer authentication, a mechanism found in architectures like ARM, which calculates a cryptographic signature for a pointer and embeds it into unused high-order bits. This signature is then checked upon dereferencing the pointer. DMAUTH extends this to DMA pointers, allowing the kernel to sign pointers before they are used by peripherals. This ensures that only legitimate, kernel-approved pointers can initiate DMA operations.
- Hardware Authenticator for On-Bus Enforcement: A critical component of DMAUTH is a dedicated hardware authenticator placed strategically on the bus, between the PCI-e bus and the DRAM controller. This authenticator intercepts all data transfers initiated by peripherals. It retrieves metadata associated with the signed DMA pointer and performs real-time bounds checking and pointer authentication. Only authenticated and in-bounds DMA transactions are permitted to proceed to DRAM; malicious or forged requests trigger an interrupt to the CPU, identifying the offending device.
- Arithmetic Capable Pointer Authentication (ACPA): A significant challenge for applying pointer authentication to DMA is the prevalence of pointer arithmetic (i.e., using offsets from a base address). Traditional pointer authentication would break if the pointer value changed due to an offset. DMAUTH introduces Arithmetic Capable Pointer Authentication (ACPA). Instead of signing the entire pointer, the kernel selectively signs a portion of the pointer's high-bits, along with specific metadata and a boot-time key. This design ensures that pointer arithmetic within the valid buffer offset does not invalidate the authentication signature, while still protecting against arbitrary pointer forging.
- Comprehensive Metadata Management: For each DMA mapping, the kernel generates and stores crucial metadata. This includes read/write permissions, the length of the allowed offset, a unique random identifier, and the precise bounds (start and end addresses) of the DMA buffer. This metadata is stored in dedicated, secure hardware storage and indexed using the signature embedded in the signed pointer. This granular information is vital for the hardware authenticator to perform accurate bounds checking and re-authentication.
- Resolution of IOMMU Vulnerabilities:
- Spatial Vulnerability: DMAUTH effectively resolves the spatial vulnerability by implementing byte-grain bounds checking. Because the kernel provides precise buffer bounds in the metadata, the hardware authenticator can verify that every DMA transaction falls strictly within the intended buffer, preventing access to other kernel data or pointers residing in the same page.
- Temporal Vulnerability: The temporal vulnerability is addressed through the inclusion of a randomized identifier within the metadata. This identifier is rerandomized every time a buffer is remapped. Since this identifier participates in the signature calculation, changing it immediately invalidates any outdated or stale signed pointers that might still be cached by a peripheral or an IOTLB, thus preventing access to unmapped memory regions.
- Exceptional Performance and Transparency: A key finding from the evaluation is DMAUTH's remarkably low overhead. It introduces only a 1% throughput overhead and a 1.8% CPU time overhead. This is significantly smaller than the overhead typically introduced by IOMMUs (which the researchers' baseline showed at 5.8% throughput and 5.6% CPU time overhead). Furthermore, DMAUTH is designed to be transparent to existing hardware and requires zero driver modification, making it highly practical for adoption without extensive re-engineering.
These findings demonstrate that DMAUTH provides a superior security posture against DMA attacks compared to IOMMUs, offering fine-grained control and immediate invalidation capabilities, all while maintaining high performance and ease of integration.
Technical Deep Dive
▶ Watch: Arithmetic capable pointer authentication innovation (6:00)
The technical foundation of DMAUTH is built upon a sophisticated interplay between software-managed pointer signing and hardware-enforced authentication. At its core, it adapts the concept of pointer authentication (PA), which is a security feature present in modern ARM architectures. In PA, a cryptographic signature (or "PAC" – Pointer Authentication Code) is generated for a pointer based on its value, a context value, and a secret key. This PAC is then embedded into unused bits of the pointer itself (typically the high-order bits). Before the pointer is dereferenced, the PAC is re-calculated and verified. If the PAC does not match, it indicates a potential pointer forgery or corruption.
DMAUTH applies this principle to DMA pointers, but with crucial modifications to suit the unique challenges of peripheral memory access. The workflow is meticulously designed:
- Kernel Object Allocation and Buffer Mapping: The process begins when the kernel allocates an object that contains an I/O buffer intended for DMA. Crucially, any other memory areas within the same page that should not be accessible by DMA are implicitly protected. The kernel then maps this I/O buffer for a specific peripheral, obtaining the corresponding DMA pointer that the device will use.
- Metadata Generation and Storage: For each newly mapped DMA buffer, the kernel generates a comprehensive set of metadata. This metadata includes:
- Read/write permissions: Specifying whether the peripheral can read from, write to, or both.
- Length of the offset: Crucial for the Arithmetic Capable Pointer Authentication (ACPA).
- Random identifier: A unique, randomized value generated for each mapping, essential for temporal protection.
- Buffer bounds: The precise start and end addresses of the legitimate DMA buffer.
This metadata is then securely stored in a dedicated hardware storage component, managed by the CPU via Memory-Mapped I/O (MMIO), making it ready to be referenced during authentication.
- DMA Pointer Signing: Before the DMA pointer is passed to the peripheral, the kernel signs it. This signing process involves the DMA pointer itself, the associated metadata, and a secret key generated at boot time. The resulting signature (PAC) is embedded into the high-order unused bits of the DMA pointer.
- Peripheral DMA Request: The signed DMA pointer is then sent to the peripheral. When the peripheral initiates a DMA transaction using this signed pointer, the request travels across the PCI-e bus.
- Hardware Authenticator Interception and Verification: This is where DMAUTH's hardware component, the authenticator, comes into play. Positioned strategically on the bus, between the PCI-e bus and the DRAM controller, the authenticator intercepts all data transfers originating from the PCI-e bus.
- It first extracts the embedded signature from the incoming signed DMA pointer.
- Using this signature as an index, it retrieves the corresponding metadata from its secure, dedicated storage.
- The authenticator then performs two critical checks:
- Bounds Checking: It verifies if the DMA request (including any offset) falls strictly within the legitimate buffer bounds specified in the retrieved metadata. This provides byte-grain spatial protection.
- Pointer Authentication: It recalculates the signature using the pointer's high-bits, the retrieved metadata, and its internal secret key. This recalculated signature is compared against the one embedded in the incoming pointer. If they do not match, it indicates that the pointer has been forged or tampered with by the peripheral.
- Enforcement: Only if both the bounds check and pointer authentication succeed are the DMA transaction permitted to proceed to the DRAM. If either check fails, the authenticator immediately generates an interrupt to the CPU, signaling that the device is malicious and should be taken offline.
Arithmetic Capable Pointer Authentication (ACPA)
The innovation of Arithmetic Capable Pointer Authentication (ACPA) is crucial. Traditional pointer authentication schemes struggle when the pointer value changes due to arithmetic operations, as this would typically invalidate the signature. DMA operations frequently involve offsets; for example, a peripheral might access an element at base_address + offset. To accommodate this, ACPA deviates from signing the entire pointer. Instead, the kernel determines a specific length of the high-bits of the pointer to be included in the signature calculation. The signature is then generated using these selected high-bits, the metadata (including the allowed offset length), and the boot-time key. This design ensures that pointer arithmetic performed within the legitimate offset range of the buffer does not alter the significant high-bits used for the signature, thus preserving its integrity while allowing flexible access within the designated buffer.
Metadata and Vulnerability Resolution
The detailed metadata plays a pivotal role in DMAUTH's security guarantees:
- The buffer bounds enable the hardware authenticator to perform precise byte-grain bounds checking, directly resolving the spatial vulnerability of IOMMUs by preventing access to unintended data within the same memory page.
- The randomized identifier, which is re-randomized after each remapping operation, is integral to resolving the temporal vulnerability. Since this identifier participates in the signature calculation, any attempt by a peripheral to use an outdated (previously signed) pointer after the buffer has been remapped and its identifier changed will result in an authentication failure. This effectively invalidates stale pointers immediately, preventing access to unmapped or re-purposed memory regions. The identifier is also made write-only to prevent any leakage or manipulation by a malicious device.
Implementation Details
The researchers implemented DMAUTH on an FPGA as part of a custom PCI-capable research framework. This framework is based on a Rockchip SoC, which offers a fully customizable connection between the PCI-e bus and DRAM. This flexible platform allowed for the precise placement and control of the authenticator hardware. Prior to implementing DMAUTH, an IOMMU baseline was established on this framework, achieving 5.8% throughput overhead and 5.6% CPU time overhead, comparable to commercial IOMMUs. This baseline served as a crucial benchmark to demonstrate DMAUTH's superior performance. The authenticator hardware, controlled by the CPU via MMIO for metadata transfer, intercepts all data transfers from the PCI bus, ensuring authentication occurs before any data reaches DRAM.
Demo / Proof of Concept
▶ Watch: FPGA implementation and research framework (8:00)
While the talk did not feature a live, interactive demonstration in the traditional sense, the practical viability and effectiveness of DMAUTH were robustly proven through a comprehensive hardware implementation and rigorous evaluation. The researchers developed a PCI-capable research framework based on a Rockchip SoC, which provided a flexible and customizable platform. This SoC's architecture allowed for the exact placement of the DMAUTH hardware authenticator between the PCI-e bus and the DRAM controller. This setup effectively served as the proof of concept for the architecture's feasibility.
The DMAUTH system was then implemented on an FPGA within this framework. This hardware implementation demonstrated how the authenticator intercepts data transfers, retrieves metadata via the embedded signature, and performs real-time bounds checking and pointer authentication. The efficacy of this hardware-software co-design was then evaluated using real-world peripherals: a network interface card (NIC) and an NVMe storage device. These evaluations are critical as they simulate realistic operational scenarios and measure the impact on actual device performance.
The evaluation results were highly compelling, serving as the primary evidence for DMAUTH's practical benefits. The system introduced only a 1% throughput overhead and a 1.8% CPU time overhead. These figures are remarkably low, especially when compared to the IOMMU baseline established on the same framework, which showed a 5.8% throughput overhead and 5.6% CPU time overhead. This significant reduction in overhead, coupled with the enhanced security guarantees, definitively demonstrates that DMAUTH is not only a theoretically sound solution but also a highly practical and efficient one for real-world deployment. The use of real-world devices and the quantitative performance metrics confirm DMAUTH's ability to operate transparently and effectively without imposing a prohibitive performance penalty.
Defensive Implications
▶ Watch: DMATH's low overhead evaluation results (9:00)
DMAUTH represents a significant leap forward in defending against sophisticated DMA attacks, offering a robust and practical solution that addresses the fundamental weaknesses of existing IOMMU-based defenses. For security defenders, understanding and advocating for the principles embodied by DMAUTH is crucial.
First and foremost, DMAUTH provides stronger spatial and temporal guarantees than traditional IOMMUs. The implementation of byte-grain bounds checking means that even if a peripheral is compromised, it cannot access memory outside its precisely defined buffer, effectively mitigating the spatial vulnerability where sensitive kernel data might reside within the same memory page. Furthermore, the use of randomized identifiers that are re-randomized upon remapping ensures immediate invalidation of outdated DMA pointers, closing the temporal window that attackers could exploit through stale IOTLB entries. These fine-grained controls offer a level of protection previously unavailable at the hardware level.
A key defensive advantage of DMAUTH is its transparency. The architecture is designed to be transparent to existing hardware and requires zero driver modifications. This is a critical factor for adoption, as it means system designers and manufacturers could integrate DMAUTH-like capabilities into future SoC designs without necessitating a complete overhaul of the vast ecosystem of device drivers. This ease of integration significantly lowers the barrier to deploying enhanced DMA security.
The minimal performance overhead (1% throughput, 1.8% CPU time) observed in the evaluation is another compelling defensive implication. High-performance computing, data centers, and embedded systems often cannot tolerate significant performance penalties for security. DMAUTH demonstrates that robust hardware-enforced security against DMA attacks can be achieved with negligible impact on system throughput and CPU utilization, making it a viable and attractive option for a wide range of platforms.
What defenders should do with this information:
- Be aware of IOMMU limitations: Understand that IOMMUs, while essential, are not foolproof against determined DMA attacks, particularly those exploiting spatial and temporal vulnerabilities.
- Advocate for hardware-backed solutions: Promote the integration of hardware-software co-designs like DMAUTH into future SoC architectures. This type of hardware-enforced security provides a much stronger foundation than purely software-based mitigations.
- Encourage research and development: Support ongoing research into hardware-level security mechanisms that provide fine-grained control and immediate enforcement.
- Consider principles for future designs: For system architects and hardware engineers, the principles behind DMAUTH — pointer authentication, byte-grain bounds checking, and dynamic identifier-based invalidation — should be considered for inclusion in next-generation platforms to enhance DMA security.
- Monitor for commercial adoption: Keep an eye out for commercial processors or platforms that begin to incorporate similar hardware-level DMA protection features, as these would offer a significantly improved security posture.
In essence, DMAUTH provides a blueprint for building more resilient systems against a class of attacks that directly targets the hardware-software interface, offering a powerful tool for defenders to secure the underlying memory access pathways.
Key Takeaways
- DMA attacks exploit inherent spatial and temporal vulnerabilities in traditional IOMMU-based defenses, which operate at page granularity and suffer from batched IOTLB invalidation.
- DMAUTH is a novel hardware-software co-design that defeats DMA attacks more effectively than IOMMUs by employing pointer authentication and fine-grained access control.
- It introduces Arithmetic Capable Pointer Authentication (ACPA), a key innovation that supports pointer arithmetic (offsets) while maintaining pointer integrity against forgery.
- DMAUTH resolves the spatial vulnerability through byte-grain bounds checking and the temporal vulnerability through randomized identifiers that immediately invalidate outdated DMA pointers.
- The system demonstrates exceptionally low overhead, with only 1% throughput overhead and 1.8% CPU time overhead, making it highly practical for real-world deployment.
- DMAUTH is designed to be transparent to existing hardware and requires zero driver modification, significantly easing its potential adoption into current and future computing platforms.
About the Speaker(s)
The talk was presented by Xingkai Wang. Based on the transcript, he is the author of the paper describing DMAUTH. No further specific details about his title or affiliation were provided within the transcript or metadata.
Reviews
Dr. Zero (Offensive Security Researcher) — MUST SEE
This talk introduces DMAUTH, a critical hardware-software co-design that fundamentally addresses long-standing spatial and temporal vulnerabilities in IOMMU-based DMA protection. Its novel application of pointer authentication, especially Arithmetic Capable Pointer Authentication (ACPA), coupled with byte-grain enforcement and immediate pointer invalidation, offers a robust, low-overhead solution to a pervasive hardware-level threat. This is a significant advancement in system security that demands attention from anyone designing or securing modern platforms.
Heather Calloway (CISO) — STRONG ACCEPT
DMAUTH presents a critical hardware-software co-design that directly addresses persistent DMA attack vulnerabilities beyond the capabilities of traditional IOMMUs. Its novel byte-grain protection and dynamic pointer invalidation, combined with negligible performance overhead and transparent integration, offer a compelling blueprint for securing future computing platforms against fundamental hardware risks. This work provides a clear path to significantly enhance system resilience from the ground up.