SeaK: Rethinking the Design of a Secure Allocator for OS Kernel
Zicheng Wang, Yicheng Guang, Yueqi Chen, Zhenpeng Lin, Michael Le, Dang K Le, Dan Williams, Xinyu Xing, Zhongshu Gu, Hani Jamjoom
33rd USENIX Security Symposium · Day 1 · USENIX Security '24 · USENIX Security '24
Overview
The talk "SeaK: Rethinking the Design of a Secure Allocator for OS Kernel" introduces a novel approach to mitigating kernel heap exploits by focusing on the selective protection of "exploit-critical objects." Presented by Zicheng Wang and a team of researchers from Nankai University, SE Border, Northwestern University, IBM, and Virginia Tech, SeaK addresses a fundamental dilemma in operating system security: the persistent tradeoff between the performance overhead and the effectiveness of kernel heap hardening mechanisms. The team's work earned all three badges from the USENIX AE committee, highlighting its practical significance and robust implementation.
Key moments
- 0:00 Introduction to Linux kernel heap exploits
- 2:00 Limitations of existing Linux kernel hardenings
- 2:50 Key insight: only protect exploit-critical objects
- 4:00 SeaK's on-demand secure allocator design
- 8:20 Demo: Preventing Dirty Cred exploit
- 8:50 Effectiveness and performance evaluation results
- 10:20 Summary of SeaK's key contributions
SeaK: Rethinking the Design of a Secure Allocator for OS Kernel
Speakers: Zicheng Wang, Yicheng Guang, Yueqi Chen, Zhenpeng Lin, Michael Le, Dang K Le, Dan Williams, Xinyu Xing, Zhongshu Gu, Hani Jamjoom
Conference: USENIX Security '24
YouTube: https://www.youtube.com/watch?v=8P1IbL8L4oY
Overview
The talk "SeaK: Rethinking the Design of a Secure Allocator for OS Kernel" introduces a novel approach to mitigating kernel heap exploits by focusing on the selective protection of "exploit-critical objects." Presented by Zicheng Wang and a team of researchers from Nankai University, SE Border, Northwestern University, IBM, and Virginia Tech, SeaK addresses a fundamental dilemma in operating system security: the persistent tradeoff between the performance overhead and the effectiveness of kernel heap hardening mechanisms. The team's work earned all three badges from the USENIX AE committee, highlighting its practical significance and robust implementation.
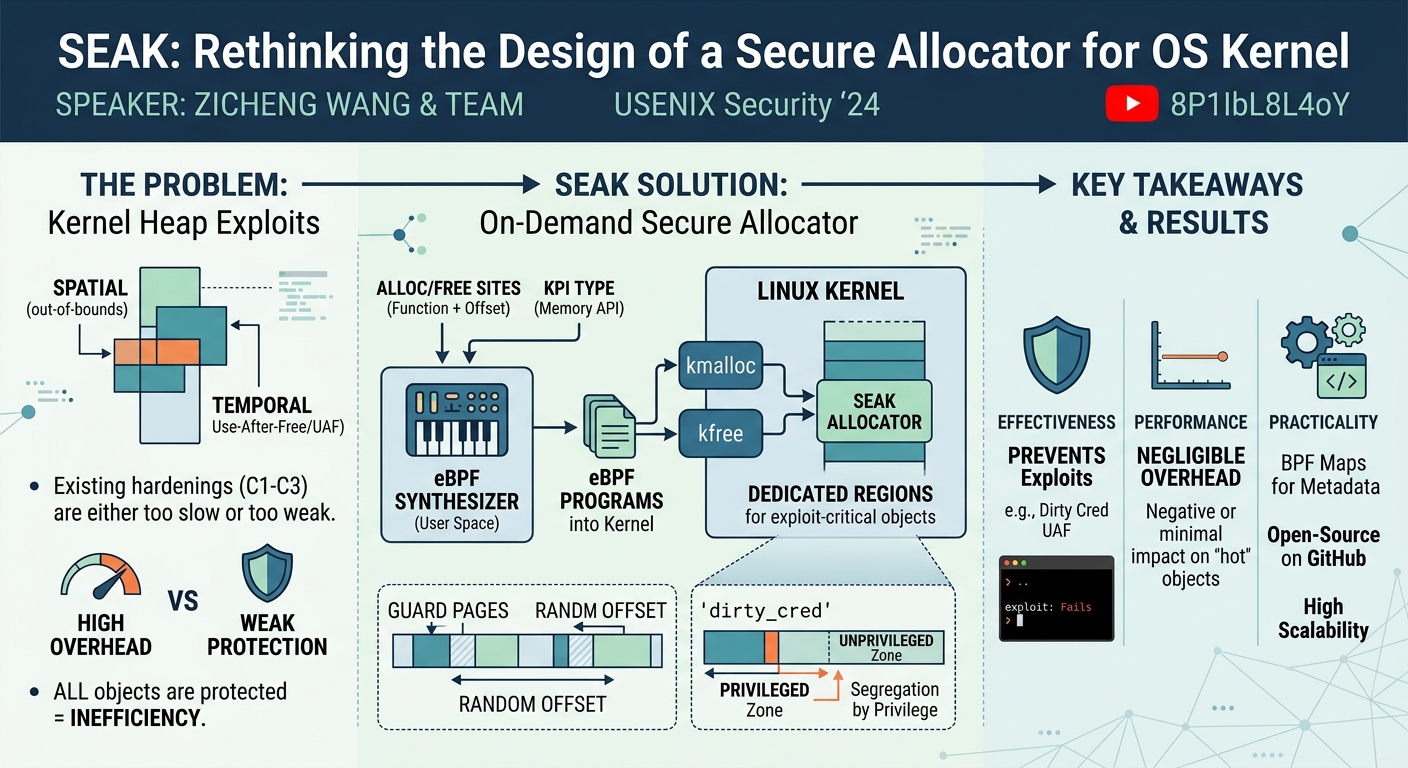
SeaK proposes an on-demand secure allocator that leverages eBPF (extended Berkeley Packet Filter) to dynamically instrument the Linux kernel. Unlike traditional hardening techniques that attempt to protect all kernel objects—often at a prohibitive performance cost—SeaK intelligently identifies and isolates only those objects that are either vulnerable to exploitation or serve as crucial targets for attackers. This targeted strategy aims to deliver high exploit prevention capabilities with negligible performance overhead, thereby presenting a viable path for enhancing kernel security in production environments.
This article delves into the intricacies of SeaK, exploring its design principles, technical implementation, and demonstrated effectiveness against real-world kernel exploits. The work builds upon recent advancements in eBPF, offering a solid foundation for its dynamic and efficient operation. By rethinking the scope of protection, SeaK offers a compelling solution to a long-standing challenge in OS kernel security, potentially preventing future exploitation campaigns that rely on heap manipulation.
Background
▶ Watch: Introduction to Linux kernel heap exploits (0:00)
Kernel heap exploits represent a significant threat vector, enabling attackers to gain elevated privileges, achieve arbitrary code execution, or cause system instability. These exploits primarily fall into two categories: spatial corruption and temporal corruption. Spatial corruption, commonly manifested as out-of-bounds access, involves writing beyond the allocated boundaries of an object, corrupting adjacent data. Temporal corruption, such as use-after-free (UAF) vulnerabilities, occurs when memory is freed but a pointer to it remains, allowing a subsequent allocation to reuse that memory and potentially overwrite sensitive data through the stale pointer. Both types of exploits often involve an "overlapping" scenario, where corruptions introduced by a vulnerable object impact sensitive data within a victim object, sometimes within the same memory cache (within-cache) or across different caches (cross-cache).
Existing Linux kernel hardening mechanisms attempt to counter these threats, but they face considerable limitations. The presenters categorize these mechanisms into three types:
- C1 (Default Enabled): Hardenings enabled by default are often widely bypassed due to their general nature and the sophisticated techniques employed by attackers.
- C2 (Default Disabled): Features like KASAN (Kernel Address SANitizer) offer robust protection but are typically too heavy for production systems. KASAN, for instance, can only protect a small portion of target objects effectively without incurring significant overhead. Other techniques like structure layout randomization (SRL) face challenges in securely storing and managing random seeds.
- C3 (Lightweight Debugging): Tools like SLAB_DEBUG are primarily intended for debugging. While they can prevent most exploits during development, they often fail against advanced attacks like dirty_cred due to their inherent design limitations and, critically, impose a significant performance overhead, sometimes up to 177% as measured by the researchers. This makes them unsuitable for deployment in live systems.
The core insight derived from this analysis is that a persistent tradeoff exists between performance overhead and effectiveness. If a hardening mechanism aims for low overhead, its effectiveness is often compromised. Conversely, high effectiveness typically comes with an unaffordable performance cost. This dilemma arises because most existing approaches attempt to protect every kernel object. The SeaK team posits that this comprehensive protection is unnecessary and impractical. Instead, they argue that what truly matters are exploit-critical objects—those that are either vulnerable to a specific bug or serve as a sensitive target (victim) for an exploit. The challenge, however, lies in precisely identifying these objects, as vulnerable objects vary with each bug, and new victim objects are continuously discovered, making it impossible to maintain an "oracle set" of all such critical objects. This fundamental problem forms the basis for SeaK's innovative, on-demand approach.
Key Findings
▶ Watch: Key insight: only protect exploit-critical objects (2:50)
SeaK introduces a paradigm shift in kernel memory security by proposing an on-demand secure allocator designed to protect exploit-critical objects with minimal overhead. The key findings and contributions of this work can be summarized by its three defining features: protection on demand, type granularity (referred to as "Atomic elevation"), and dynamic enforcements.
The central idea is to selectively protect only those kernel objects that are deemed critical for an exploit chain, rather than attempting to secure the entire kernel heap. This selectivity is achieved through several innovative mechanisms:
- Exploit-Critical Object Identification: While acknowledging the difficulty of a priori identification, SeaK focuses on protecting objects once a vulnerability or a critical victim type is identified, allowing for a reactive yet highly effective defense. This is exemplified by its ability to protect specific
struct fileobjects when a vulnerability likedirty_credis known. - eBPF as the Enforcement Mechanism: SeaK leverages eBPF to dynamically instrument the kernel. Instead of modifying the kernel source code, eBPF programs are synthesized in user space and loaded into the kernel, where they can intercept and replace standard memory allocation functions like
kmallocandkfreewith SeaK's secure allocation strategy. This allows for flexible, low-overhead, and hot-patchable security policies. - BPF Maps for Metadata Management: The system utilizes BPF Maps to store and manage metadata related to dedicated regions and isolated objects. These maps enable efficient lookup and management of security policies and allocated memory segments within the kernel.
- Dedicated Regions and Isolation Techniques: SeaK allocates exploit-critical objects into special "dedicated regions." Within these regions, two primary isolation techniques are employed:
- Guard pages: These are placed around allocated objects to prevent spatial corruption (e.g., out-of-bounds writes) from spilling over into adjacent memory, thus protecting other objects or critical kernel data.
- Random offset: Within a dedicated region, objects are allocated with a random offset. This technique significantly complicates temporal corruption (e.g., use-after-free) by making it difficult for an attacker to reliably re-allocate a new object at the exact memory address of a previously freed, vulnerable object.
- Demonstrated Effectiveness and Efficiency: The research team demonstrated SeaK's ability to successfully prevent well-known kernel exploits, including the infamous dirty_cred (a use-after-free vulnerability). This was achieved by using object privilege as a key for segregation, ensuring that
struct fileobjects with different privilege levels were allocated in distinct memory regions, thereby preventing their temporal overlapping. Furthermore, SeaK exhibited negligible performance overhead even for frequently allocated ("hot") objects, with some measurements showing negative overhead (attributed tomembenchfluctuations), and minimal memory usage, even in scenarios with 64 concurrent cases. Its high scalability was also confirmed. - Open-Source Contribution: SeaK provides an open-source design and implementation on GitHub, encouraging broader adoption, reproduction of experiments, and further community development.
These findings collectively highlight SeaK as a practical, high-performance, and highly effective solution for mitigating kernel heap exploits, addressing the limitations of prior hardening efforts.
Technical Deep Dive
▶ Watch: SeaK's on-demand secure allocator design (4:00)
SeaK's technical architecture is built upon the intelligent use of eBPF for dynamic kernel instrumentation and a sophisticated memory allocation strategy that isolates exploit-critical objects. The design can be broken down into two main components: the eBPF Synthesizer in user space and the runtime separation mechanisms enforced within the kernel.
eBPF Synthesizer
The eBPF Synthesizer operates in user space and is responsible for generating the eBPF programs that will be loaded into the kernel. This synthesis process requires two primary inputs:
- Function + Offset (Allocation and Free Sites): These inputs specify the exact locations within the kernel code where memory allocation (
kmalloc,kmem_cache_alloc, etc.) and deallocation (kfree) functions are called. By identifying these sites, SeaK can precisely hook into the kernel's memory management operations. - KPI Type (Kernel API Type): This input defines the specific kernel memory allocation API being used. Different kernel APIs have distinct prototypes, meaning they expect parameters in different orders or encapsulate object size within different data structures. For example:
- For
kmalloc, the object size is typically the first parameter passed to the function. - For
kmem_cache_alloc, the object size is often a field within thekmem_cachestructure itself, which is passed as a parameter.
The synthesizer must account for these variations to correctly extract the object size, which is crucial for determining the appropriate allocation strategy.
Based on these inputs, the synthesizer generates tailored eBPF programs. These programs are designed to replace the default kmalloc and kfree calls with SeaK's custom logic, ensuring that designated exploit-critical objects are handled by the secure allocator. This dynamic instrumentation allows SeaK to apply its protections without requiring kernel recompilation or modification of the kernel's source code, making it highly flexible and deployable.
Runtime Separation
Once the eBPF programs are loaded, they enforce SeaK's secure allocation strategy at runtime within the kernel. This involves managing memory through BPF Maps and isolating objects in dedicated regions.
- BPF Maps: SeaK utilizes two primary BPF Maps:
region_to_index: This map is used to look up and manage dedicated memory regions. Its keys are a composite of the Instruction Pointer (IP) (representing the allocation site), the object size, and the privilege zone of the object. By incorporating these elements into the key, SeaK can ensure that objects allocated from specific code locations, of specific sizes, and with particular privilege levels are directed to distinct dedicated regions.object_to_region: This map stores metadata about individual allocated objects, allowing SeaK to quickly look up the associated dedicated region and its properties based on the object's memory address. This is critical for efficient deallocation and consistency checks.
- Dedicated Regions and Isolation: When an exploit-critical object is identified for protection, SeaK allocates it within a dedicated region. These regions are fortified with two key isolation mechanisms:
- Guard Pages: These are unmapped or protected memory pages placed immediately adjacent to the dedicated region or individual objects within it. Their purpose is to detect and prevent spatial corruption. If an attacker attempts an out-of-bounds write beyond the intended boundaries of an object, they will hit a guard page, triggering a page fault and aborting the exploit attempt. This effectively contains the impact of spatial vulnerabilities.
- Random Offset: Within a dedicated region, objects are not allocated at predictable, contiguous addresses. Instead, they are placed with a random offset. This mechanism is primarily designed to counter temporal corruption, particularly use-after-free exploits. When an object is freed, and an attacker attempts to re-allocate memory at the same address to overwrite it, the random offset makes it extremely difficult to reliably hit the previously freed memory slot. This unpredictability significantly raises the bar for temporal exploits.
Example: Dirty Cred Exploit Protection
The presentation highlights the effectiveness of SeaK against the dirty_cred exploit, a classic example of a use-after-free vulnerability that allows for privilege escalation.
- Nature of the Exploit:
dirty_credinvolves a temporal overlapping between objects of different privileges. Typically, astruct fileobject representing a privileged file is freed, leaving a dangling pointer. Subsequently, an attacker triggers the allocation of an unprivilegedstruct file(or similar object) that reuses the memory previously occupied by the privileged file. The dangling pointer then allows the attacker to manipulate the newly allocated, unprivileged object as if it were the original privileged one, leading to privilege escalation (e.g., gaining root access). - SeaK's Protection: SeaK leverages the
privilegeof the object as a crucial component of the key for theregion_to_indexmap. By doing so,struct fileobjects with different privilege levels (e.g., a privileged root-owned file vs. an unprivileged user-owned file) are allocated into distinct dedicated regions. This separation fundamentally prevents the temporal overlap required by thedirty_credexploit. Even if a privilegedstruct fileis freed, an attacker cannot easily re-allocate an unprivilegedstruct filein the same dedicated region, thereby thwarting the exploit's core mechanism. - Implementation Details: The eBPF program for
dirty_credprotection is synthesized using information from bug reports, specifically the allocation site and free site of thestruct fileobject. This precise targeting ensures that only the relevant allocation/free paths are instrumented, minimizing overhead.
This detailed approach, combining dynamic eBPF instrumentation with intelligent memory segregation and isolation techniques, underpins SeaK's ability to provide robust protection against complex kernel heap exploits.
Demo / Proof of Concept
▶ Watch: Effectiveness and performance evaluation results (8:50)
The talk included a compelling live demonstration that visually validated SeaK's effectiveness against real-world kernel exploits. The demonstration involved a scenario where an attacker attempted to exploit a vulnerability, likely the dirty_cred use-after-free exploit, to gain root privileges.
The demo was structured to showcase two distinct outcomes:
- With SeaK Protection Enabled: The presenter first activated SeaK's protection mechanisms. When the exploit was then launched, the system successfully detected and prevented the attack. The output on the screen explicitly indicated that the exploit "fails," confirming that SeaK's secure allocator had intercepted the malicious memory manipulation attempt.
- With SeaK Protection Disabled: To illustrate the vulnerability without SeaK, the presenter then deactivated the protection. Upon re-executing the identical exploit, it successfully bypassed the default kernel defenses. The terminal output clearly showed the attacker gaining elevated privileges, culminating in access to a
root@pinbashshell. This stark contrast unequivocally demonstrated SeaK's capability to mitigate critical kernel exploits that would otherwise succeed.
This proof-of-concept provided strong empirical evidence of SeaK's practical applicability and its ability to prevent a significant class of kernel heap vulnerabilities, specifically temporal corruptions like use-after-free, by separating objects based on their properties and privileges. The clear and immediate failure of the exploit when SeaK was active, juxtaposed with its success when SeaK was disabled, served as a powerful validation of the research team's claims regarding effectiveness.
Defensive Implications
▶ Watch: Summary of SeaK's key contributions (10:20)
SeaK offers significant defensive implications for system administrators, security engineers, and kernel developers striving to enhance the security posture of Linux-based systems. Its core principle of on-demand, targeted protection provides a pragmatic alternative to the often-impractical all-encompassing hardening solutions.
Here are key defensive implications:
- Prioritize Exploit-Critical Objects: Defenders should shift their focus from attempting to protect every kernel object to identifying and prioritizing exploit-critical objects. This includes objects known to be vulnerable (e.g., those associated with disclosed CVEs) or objects that serve as sensitive targets for privilege escalation (e.g.,
struct cred,struct file). SeaK's approach provides a framework for how to implement this selective protection effectively. - Leverage eBPF for Dynamic Hardening: The use of eBPF is a game-changer. It allows for dynamic instrumentation of the kernel without requiring recompilation or reboots, making security updates and targeted mitigations far more agile. Security teams can develop and deploy eBPF-based policies to intercept and modify kernel behavior, such as memory allocation, in response to newly discovered vulnerabilities or evolving threat landscapes. This capability enables a more proactive and adaptive defense strategy.
- Implement Allocation Site and Type-Aware Policies: SeaK's reliance on
function + offset(allocation sites) andKPI type(kernel API type) for synthesizing eBPF programs emphasizes the importance of understanding the precise context of kernel memory allocations. Defenders should analyze bug reports and vulnerability disclosures to identify these specific allocation and free sites, allowing them to craft highly targeted security policies. - Segregate Objects by Privilege and Type: The success against dirty_cred highlights the effectiveness of segregating objects based on their privilege levels or other critical properties. Implementing custom allocators or eBPF-based hooks that ensure objects with different security contexts (e.g., privileged vs. unprivileged, network buffers vs. file system objects) are allocated in distinct memory regions can significantly reduce the attack surface for temporal exploits.
- Utilize Guard Pages and Random Offsets: These fundamental memory protection techniques, employed by SeaK, should be considered for any custom or enhanced memory allocator. Guard pages are crucial for preventing spatial corruptions from cascading, while random offsets within allocated regions are vital for disrupting temporal exploits like use-after-free by introducing unpredictability.
- Embrace Open-Source Contributions: SeaK's open-source nature means its design and implementation can be studied, adapted, and integrated into existing security pipelines. Organizations can contribute to its development, extend its capabilities, or use it as a blueprint for building their own tailored secure allocators.
- Consider Performance vs. Security Tradeoffs Realistically: SeaK demonstrates that high security does not necessarily demand prohibitive performance overhead. By being selective and efficient, it achieves strong protection with negligible impact, challenging the long-held belief that a significant tradeoff is inevitable. This encourages defenders to re-evaluate their security strategies with a fresh perspective on what is achievable.
In essence, SeaK provides a blueprint for a modern, efficient, and highly effective kernel hardening strategy. By moving beyond blanket protection to intelligent, on-demand mitigation, it empowers defenders to build more resilient and secure operating systems against sophisticated heap-based attacks.
Key Takeaways
- Existing Linux kernel heap hardening mechanisms face a fundamental and persistent tradeoff between performance overhead and exploit prevention effectiveness.
- SeaK proposes an innovative on-demand secure allocator that focuses protection specifically on "exploit-critical objects" (vulnerable or victim objects) rather than attempting to secure the entire kernel heap.
- The system leverages eBPF for dynamic kernel instrumentation, allowing it to intercept and replace standard
kmallocandkfreecalls with custom, secure allocation logic without modifying kernel source code. - SeaK employs dedicated memory regions fortified with guard pages (to prevent spatial corruption) and random offsets (to prevent temporal corruption like use-after-free) to isolate critical objects.
- It successfully prevents real-world exploits like dirty_cred by segregating objects based on properties such as privilege, ensuring that objects with different security contexts are allocated in distinct memory regions.
- SeaK demonstrates negligible performance overhead (even for frequently allocated objects) and minimal memory usage, making it a practical and scalable solution for production environments.
- The project provides an open-source design and implementation, encouraging community adoption, further research, and the development of more robust kernel security measures.
About the Speaker(s)
The primary presenter for "SeaK: Rethinking the Design of a Secure Allocator for OS Kernel" was Zicheng Wang. The work is a collaborative effort involving a distinguished team of researchers from multiple institutions, including Nankai University, SE Border, Northwestern University, IBM, and Virginia Tech. The full list of speakers and contributors includes Zicheng Wang, Yicheng Guang, Yueqi Chen, Zhenpeng Lin, Michael Le, Dang K Le, Dan Williams, Xinyu Xing, Zhongshu Gu, and Hani Jamjoom. This diverse group of experts brings together significant knowledge in operating system security, memory management, kernel internals, and eBPF technology, reflecting the interdisciplinary nature and depth of the research presented. Their collective expertise underscores the rigor and comprehensive approach taken in designing and implementing SeaK.
Reviews
Dr. Zero (Offensive Security Researcher) — MUST SEE
This research introduces SeaK, a novel eBPF-driven on-demand secure allocator for the Linux kernel. By intelligently isolating "exploit-critical objects" with guard pages and random offsets, SeaK effectively mitigates kernel heap exploits like dirtycred with negligible performance overhead, offering a pragmatic and scalable solution to a persistent security dilemma.
Heather Calloway (CISO) — STRONG ACCEPT
SeaK presents a critical shift in kernel security, offering an on-demand, eBPF-driven allocator that effectively mitigates heap exploits with negligible performance overhead. This research provides a practical blueprint for defenders, enabling more targeted and agile protection against a significant class of business-critical vulnerabilities. It's a pragmatic solution addressing a long-standing tradeoff between security and performance.